How HackNotice Delivers Operational Adversary Intelligence
HackNotice continuously collects and analyzes intelligence from across the adversary ecosystem; transforming threat actor activity, breach data, and ransomware publications into operational security insights.
The platform combines large-scale intelligence collection, automated analysis, and operational workflows to help security teams detect compromise events affecting their organizations and vendors.

Turning Adversary Activity into Operational Intelligence
HackNotice collects intelligence from the sources where attackers coordinate, distribute stolen data, and announce new compromises. This intelligence is enriched, analyzed, and delivered to security teams through actionable alerts and operational workflows.
The Workflow, Not Just The Pitch
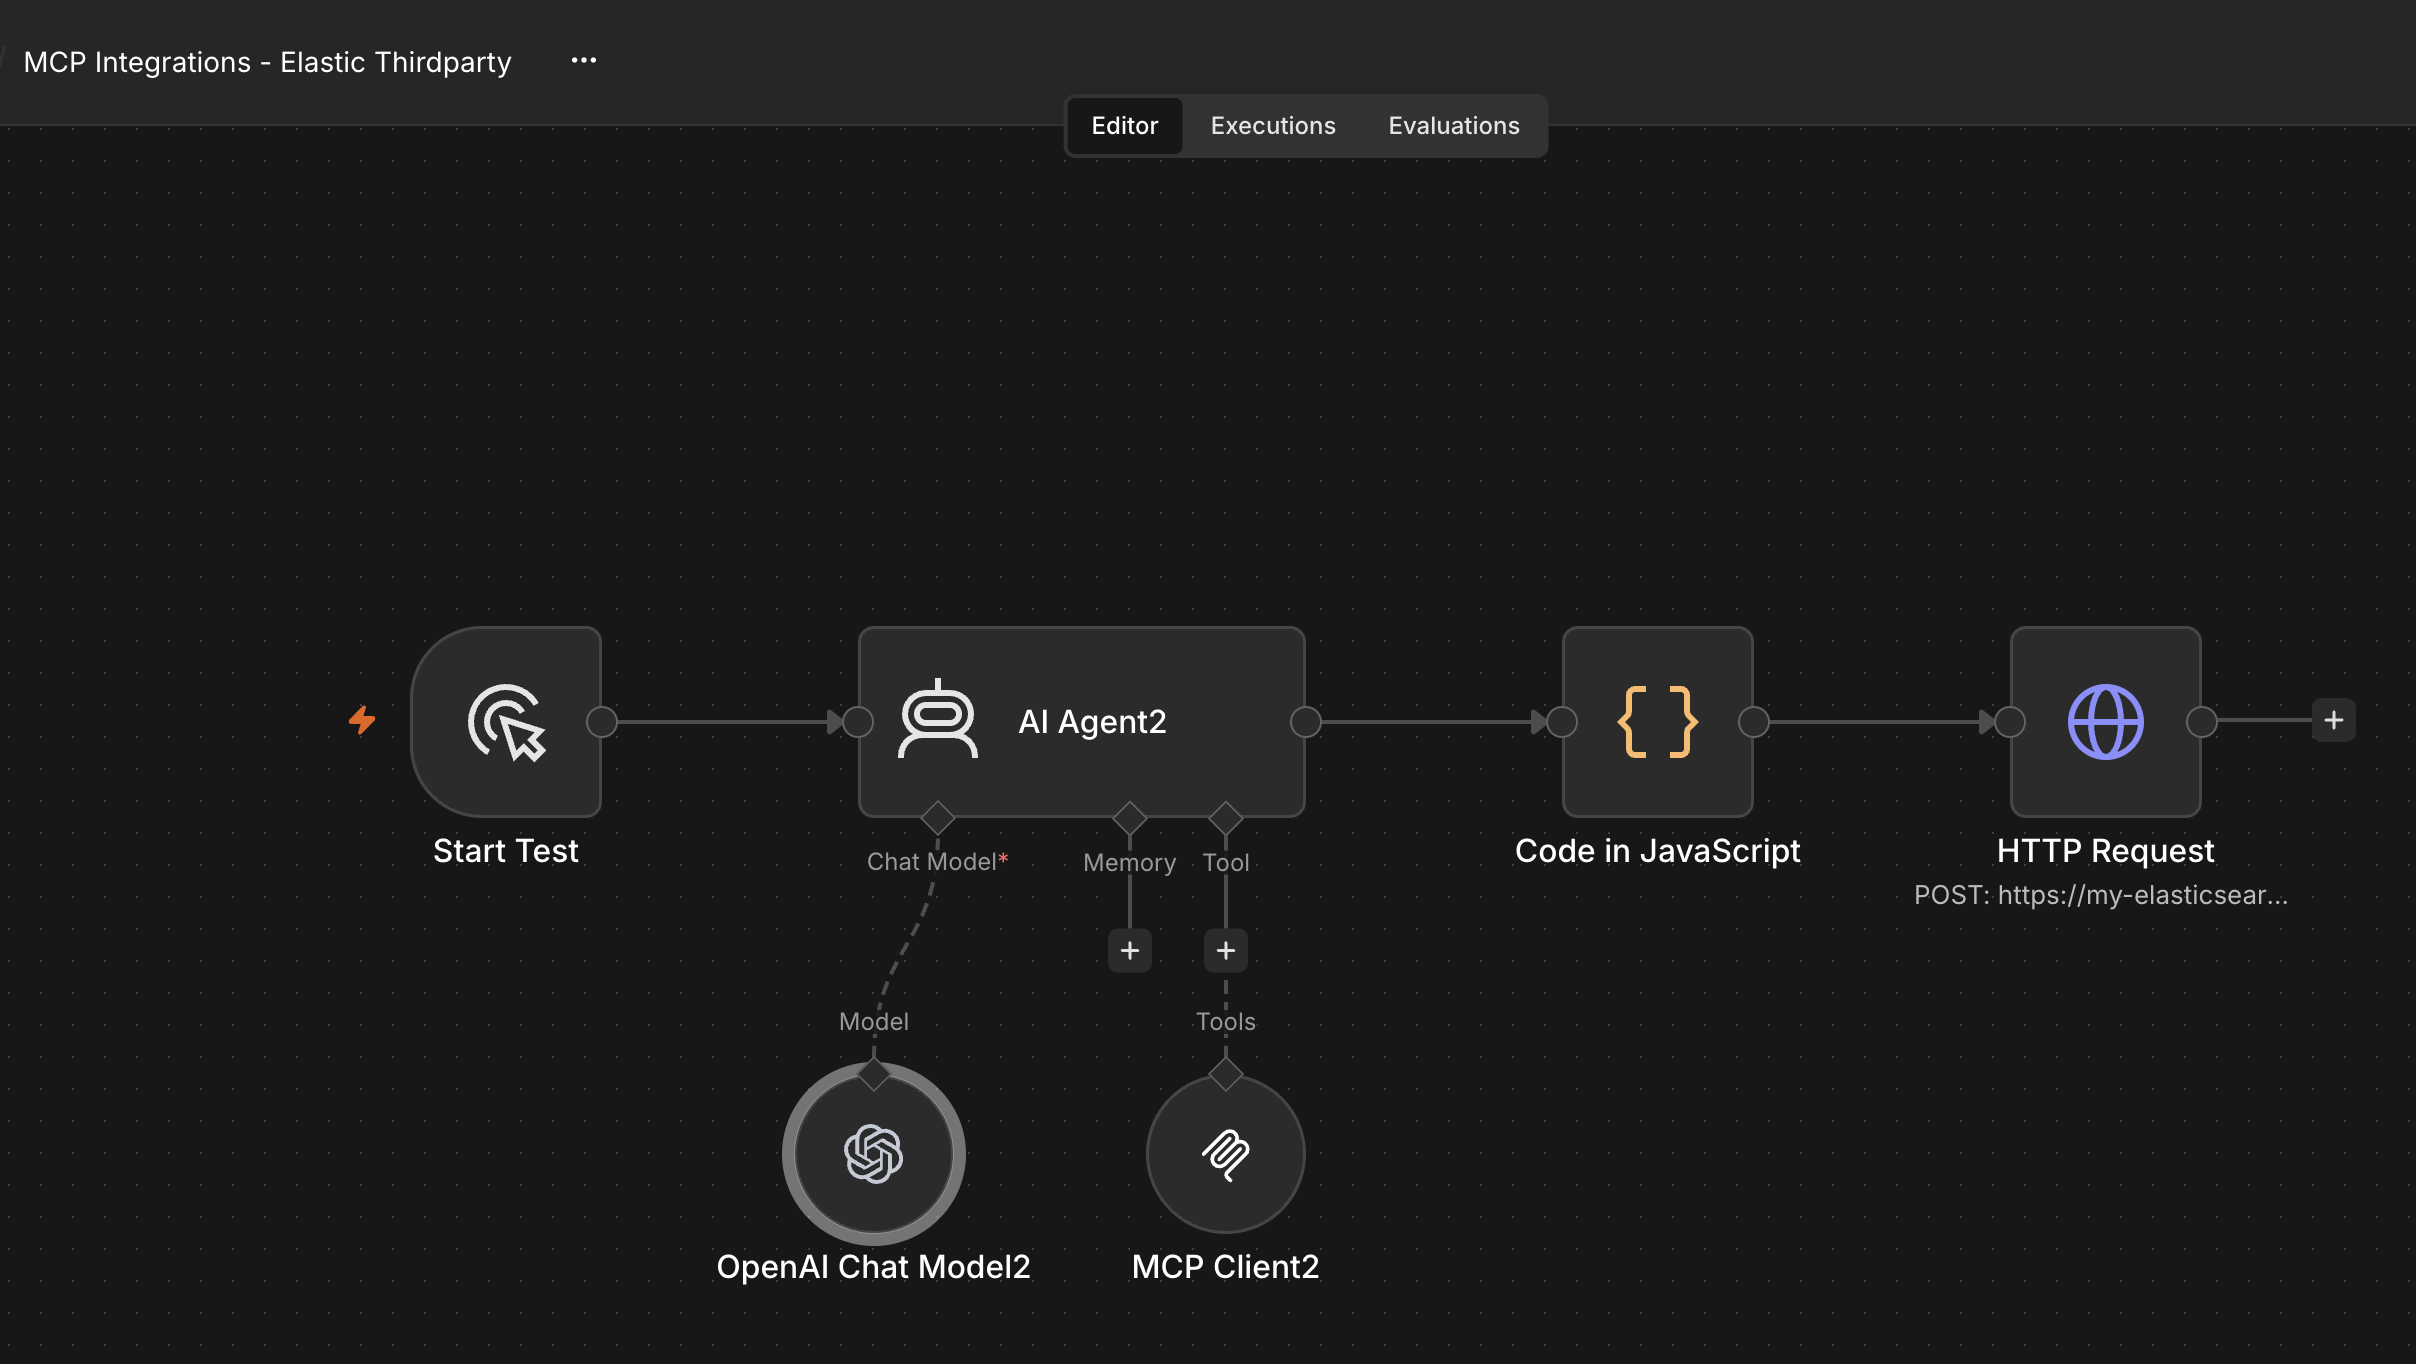
A Real Agentic Workflow, Built On MCP
This is an actual n8n automation: an AI agent using HackNotice’s MCP Client as a callable tool alongside a chat model, running real queries against live data.

Global Intelligence Collection Across the Adversary Ecosystem
HackNotice continuously collects threat intelligence from hundreds of adversary-controlled sources across the open web and underground communities.
These sources represent the environments where attackers trade stolen credentials, publish ransomware victims, distribute breach data, and discuss new attacks.
From Stolen Credential to Closed Door
An authorized agentic workflow for agentic credential defense
HackNotice converts infostealer logs and credential dumps into a controlled response workflow. Customers define exactly where testing is allowed. The HackNotice Credential Defense Agent handles the repetitive work of validating, documenting, and routing valid accounts for action.
DISCOVER
Continuously collect exposed credentials from infostealer logs and credential dumps.
AUTHORIZE
Define approved domains, applications, login URLs, authentication methods, testing types, and the historical testing window.
VALIDATE
Test exposed credentials only against customer-authorized endpoints and within the approved scope.
PROVE
Capture evidence when an exposed credential authenticates so the security team can act on a confirmed valid account.
INVALIDATE
Route the login URL and account email for password reset, session revocation, and account review. The password is never sent.
Customer-defined and reviewed
Testing types, applications, login URLs, authentication methods, and testing windows are approved before activation.
Close the access path automatically
When a valid account is confirmed, HackNotice can notify the customer’s invalidation endpoint without transmitting the password.
From Stolen Credential to Closed Door
An authorized agentic workflow for agentic credential defense
HackNotice converts infostealer logs and credential dumps into a controlled response workflow. Customers define exactly where testing is allowed. The HackNotice Credential Defense Agent handles the repetitive work of validating, documenting, and routing valid accounts for action.
DISCOVER
Continuously collect exposed credentials from infostealer logs and credential dumps.
AUTHORIZE
Define approved domains, applications, login URLs, authentication methods, testing types, and the historical testing window.
VALIDATE
Test exposed credentials only against customer-authorized endpoints and within the approved scope.
PROVE
Capture evidence when an exposed credential authenticates so the security team can act on a confirmed valid account.
INVALIDATE
Route the login URL and account email for password reset, session revocation, and account review. The password is never sent.
Customer-defined and reviewed
Testing types, applications, login URLs, authentication methods, and testing windows are approved before activation.
Close the access path automatically
When a valid account is confirmed, HackNotice can notify the customer’s invalidation endpoint without transmitting the password.
Intelligence Enrichment and Threat Context
Raw intelligence signals are analyzed and enriched to provide security teams with meaningful context about each event.
HackNotice correlates compromise indicators with threat actor activity, ransomware groups, and known adversary tactics to help security teams understand the risk associated with each alert.
Real-Time Detection of Compromise Events
HackNotice surfaces intelligence alerts when compromise indicators are detected across monitored organizations, vendors, or users.
These alerts help security teams identify potential security incidents earlier than traditional monitoring approaches.
Example Detection Events
HackNotice may alert organizations when:
- A monitored vendor appears on a ransomware leak site
- Employee credentials appear in breach datasets or infostealer logs
- Threat actors claim compromise of a monitored organization on underground forums
- Stolen data associated with an organization appears in criminal marketplaces
These signals often represent the earliest evidence of compromise activity.
Operational Workflows for Security Teams
HackNotice integrates intelligence alerts into operational workflows that support investigation, response, and vendor risk management.
These workflows help security teams quickly determine the impact of compromise events and coordinate response actions.

Integrations with Security Operations Platforms
HackNotice integrates with security operations tools so intelligence alerts can be incorporated into existing detection and response workflows.
See HackNotice Intelligence in Action
HackNotice helps security teams detect compromise events earlier, understand adversary activity, and operationalize threat intelligence across their organization and supply chain.
