REAL SECURITY STARTS WITH REAL THREATS
Automated detection of external compromise
as threats emerge.
The most significant security risks begin when attackers compromise identities, vendors, and trusted partners. HackNotice continuously discovers, investigates, and delivers actionable intelligence directly from the adversary ecosystem, helping security teams mitigate real-world risk before it becomes an incident.
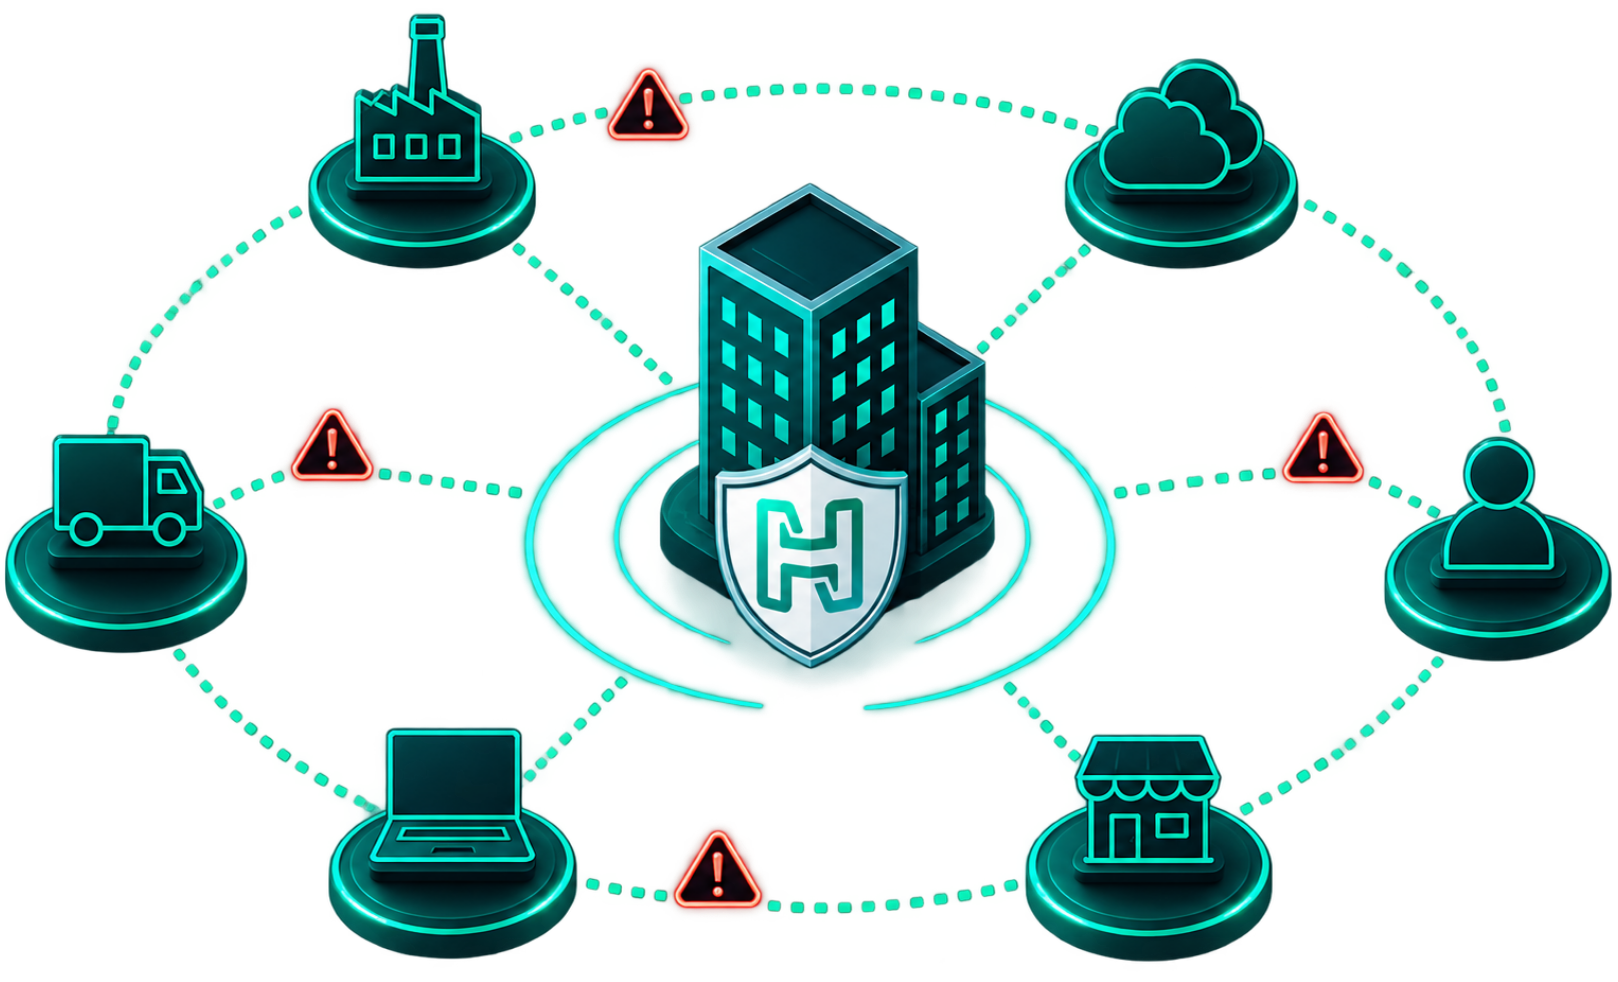
Measuring Risk Isn’t the Same as Detecting Compromise.
Security teams invest heavily in vendor questionnaires, security ratings, and compliance assessments to understand third-party risk. While these tools provide valuable governance and posture insights, they are inherently point-in-time evaluations.
They cannot detect when a vendor has already been compromised, credentials have been exposed, or threat actors have begun targeting your ecosystem.
Attackers Don’t Care About Security Ratings.
Threat actors don’t evaluate questionnaire responses or security scores before launching an attack. They exploit compromised identities, purchase stolen credentials, target trusted third parties, and publish data across ransomware sites, underground forums, and criminal marketplaces.
Detecting these real-world threats requires continuous intelligence from the adversary ecosystem, not another point-in-time assessment.
Ransomware Is the Leading Third-Party Threat
Ransomware attacks and third-party breaches are now an expected part of today’s threat landscape. HackNotice continuously detects new incidents across your supply chain and uses AI-driven investigations and automated response workflows to help your team quickly understand exposure, assess impact, and take action before threats spread further.
The Majority of Breaches Start With Compromised Credentials and Identity Attacks
Stolen credentials and identity compromise are the entry point for most third-party breaches; not misconfigured ports or missing headers. HackNotice continuously monitors for exposed credentials across your vendor and employee ecosystem, using AI-driven investigations and automated workflows to help your team verify exposure and shut it down before it’s exploited.
Avoid the noise of traditional dark web monitoring. Use agentic intelligence for actionable alerts.
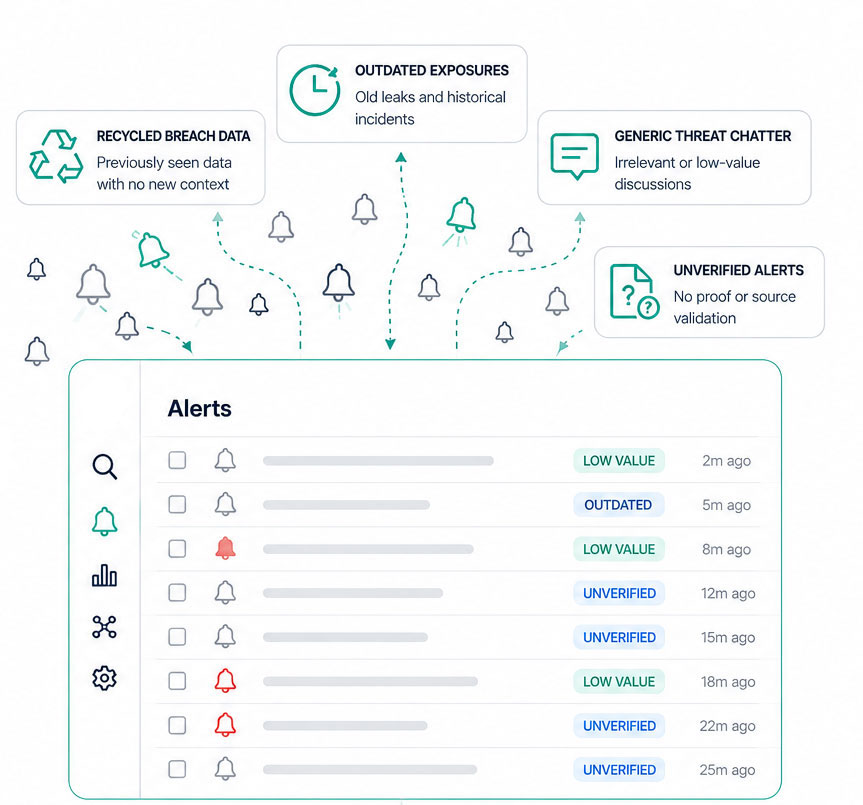
Avoid False Positives.
Automate Security Intelligence.
HackNotice doesn’t just collect alerts. We continuously discover, investigate, and prioritize real-world threats across identities, third parties, and the supply chain.
AI-driven investigations and automated workflows eliminate hours of manual research, transforming raw adversary activity into actionable intelligence your team can immediately use.
Less Time Investigating.
More Time Responding.
The Future of Security Operations and Third Party Monitoring Is Agentic.
Security teams simply need more time.
HackNotice continuously discovers, investigates, and delivers actionable intelligence across identity, third-party, and supply chain threats. AI-driven investigations and automated workflows eliminate hours of manual analysis, helping security teams detect compromise earlier, accelerate response, and scale their impact.
